%20--%3e%3cdefs%3e%3cstyle%3e%20.st0%20{%20fill:%20%23111;%20}%20.st1%20{%20fill:%20%23f0c53f;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st0'%20d='M135.48,27.83h20.93c5.71,0,16.3-2.12,17.05,6.03.5,5.47,0,11.23,0,16.71v27.98c0,5.03-.08,10.07,0,15.1,0,.03.96-1.28.97-1.28-1.04.09-2.08.83-3.2.96-.12,0-.24-.01-.36,0-1.28.11-2.63,0-3.91,0h-12.73c-4.99,0-18,2.39-20.53-3.66-.72-1.73-.45-3.99-.45-5.82V31.15c0-.72.33-2.35,0-3-.07-.13,0-.44,0-.59v-.05c-1.36,1.35-1.35,1.64.03.87.68-.4,1.41-.58,2.21-.54,1.83-.18,2.83-6.4,3.75-6.5-7.26.73-9.77,9.8-9.77,15.98v53.44c0,2.42-.25,4.87,1.41,6.88,2.29,2.78,6.04,2.2,9.24,2.2,8.86,0,17.89.53,26.73,0,6.49-.39,10.32-8.07,10.4-14.01.23-17.76,0-35.54,0-53.31,0-2.02.31-4.39-.14-6.39-1.16-5.13-6.08-4.79-10.15-4.79h-27.73c-1.67,0-3.05,6.5-3.75,6.5h0Z'/%3e%3cpath%20class='st0'%20d='M141.48,73.83h20c1.67,0,3.05-6.5,3.75-6.5h-20c-1.67,0-3.05,6.5-3.75,6.5Z'/%3e%3cpath%20class='st0'%20d='M141.48,56.86h20c1.67,0,3.05-6.5,3.75-6.5h-20c-1.67,0-3.05,6.5-3.75,6.5Z'/%3e%3cpath%20class='st0'%20d='M63.48,65.83h64c1.67,0,3.05-6.5,3.75-6.5h-64c-1.67,0-3.05,6.5-3.75,6.5Z'/%3e%3cpath%20class='st1'%20d='M97.36,74.58c6.63,0,12-5.37,12-12s-5.37-12-12-12-12,5.37-12,12,5.37,12,12,12Z'/%3e%3cpath%20class='st0'%20d='M35.46,41.08c5.18.28,9.72,3.03,11.67,7.97,2.61,6.61-1.07,10.6-7.92,10.63-4.87.02-9.43-2.94-11.43-7.37-.98-2.17-1.99-5.96-.57-8.07,1.58-2.37,5.65-3.03,8.26-3.17,1.76-.09,2.93-6.45,3.75-6.5-7.75.42-12.33,6.62-15.09,13.32-3.44,8.35,1.75,18.23,11.34,18.27,7.59.03,12.29-6.75,14.98-13.05,3.71-8.72-1.57-18.02-11.23-18.54-1.56-.08-3.18,6.53-3.75,6.5h-.01Z'/%3e%3cpath%20class='st0'%20d='M15.81,81.71c9.16-11.46,30.69-10.97,39.74.35-.22-.28,4.62-5.41,3.75-6.5-9.52-11.9-31.17-11.42-40.58.35-1.03,1.29-2.06,2.84-2.68,4.38-.12.31-1.12,2.54-.23,1.42Z'/%3e%3c/svg%3e)
%20--%3e%3cdefs%3e%3cstyle%3e%20.st0%20{%20fill:%20%23111;%20}%20.st1%20{%20fill:%20%23f0c53f;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st1'%20d='M75.35,53.07c3.07,0,5.56-2.49,5.56-5.56s-2.49-5.56-5.56-5.56-5.56,2.49-5.56,5.56,2.49,5.56,5.56,5.56Z'/%3e%3cpath%20class='st0'%20d='M89.35,50.02h24.71c1.29,0,2.36-5.02,2.9-5.02h-24.71c-1.29,0-2.36,5.02-2.9,5.02Z'/%3e%3cpath%20class='st1'%20d='M75.35,73.15c3.07,0,5.56-2.49,5.56-5.56s-2.49-5.56-5.56-5.56-5.56,2.49-5.56,5.56,2.49,5.56,5.56,5.56Z'/%3e%3cpath%20class='st1'%20d='M75.35,93.23c3.07,0,5.56-2.49,5.56-5.56s-2.49-5.56-5.56-5.56-5.56,2.49-5.56,5.56,2.49,5.56,5.56,5.56Z'/%3e%3cpath%20class='st0'%20d='M89.35,90.18h16.99c1.29,0,2.36-5.02,2.9-5.02h-16.99c-1.29,0-2.36,5.02-2.9,5.02Z'/%3e%3cpath%20class='st0'%20d='M89.35,70.1h24.71c1.29,0,2.36-5.02,2.9-5.02h-24.71c-1.29,0-2.36,5.02-2.9,5.02Z'/%3e%3cpath%20class='st0'%20d='M63.68,19.24h48c.76,0,2.22-.29,2.96,0,1.09.43,2.41,2.4,3.22,3.21,4.54,4.54,9.09,9.09,13.63,13.63,2.05,2.05,1.68,2.56,1.68,5.66v55.8c0,1.71.02,3.44,0,5.15,0,.39.02.79,0,1.18v.18c-.02.33,0,2.87-.05,1.05.05,1.61-.46.39.4.02-2.22.97-3.75,1.75-6.15,1.77-1.65.02-3.3,0-4.95,0h-53.97c-5.11,0-9.32-1.88-9.58-7.72-.13-2.87,0-5.78,0-8.66,0-22.65-.74-45.44,0-68.08.02-.43.07-1.06.05-1.41-.02-.36.53-1.62-.12-.5-.66,1.12.08.05.42-.06,1.61-.5,2.71-1.14,4.46-1.24,1.35-.07,2.26-4.98,2.9-5.02-6.29.32-10.43,7.08-10.63,12.97-.13,3.61,0,7.24,0,10.85v60.51c0,2.92-.5,6.75.85,9.43,2.3,4.59,7.62,3.93,11.9,3.93h18.97c12.22,0,24.46.11,36.68,0,5.88-.05,9.44-4.08,11.22-9.52,1.03-3.15.52-7.09.52-10.34v-57.27c0-3.07-2.14-4.14-4.34-6.34l-7.63-7.63c-1.87-1.87-3.78-4.49-5.97-5.97-2.08-1.4-5.91-.6-8.43-.6h-43.15c-1.29,0-2.36,5.02-2.9,5.02h.01Z'/%3e%3cpath%20class='st0'%20d='M114.64,19.11v18.53l.02.13h18.53c1.29,0,2.36-5.02,2.9-5.02h-15.36c-.39,0-2.9.28-3.15.05-.23-.22,0-2.39,0-2.82v-15.63c0,.76-2.93,3.17-2.93,4.76h0Z'/%3e%3c/svg%3e)
%20--%3e%3cdefs%3e%3cstyle%3e%20.st0%20{%20fill:%20%23111;%20}%20.st1%20{%20fill:%20%23f0c53f;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st0'%20d='M63.74,16.55h50.86c.81,0,2.36-.31,3.13,0,1.15.46,2.55,2.54,3.41,3.4,4.81,4.81,9.63,9.63,14.44,14.44,2.18,2.18,1.78,2.71,1.78,6v59.12c0,1.82.02,3.64,0,5.46,0,.42.02.83,0,1.25v.19c-.02.35,0,3.04-.06,1.11.06,1.7-.48.42.43.02-2.35,1.03-3.98,1.85-6.51,1.87-1.75.02-3.49,0-5.24,0h-57.18c-5.42,0-9.88-1.99-10.15-8.18-.14-3.04,0-6.13,0-9.18,0-24-.79-48.14,0-72.12.02-.46.07-1.12.06-1.49-.02-.38.56-1.72-.13-.53-.7,1.19.09.05.45-.07,1.71-.53,2.87-1.21,4.72-1.31,1.43-.07,2.4-5.28,3.07-5.32-6.67.34-11.05,7.5-11.27,13.75-.14,3.82,0,7.67,0,11.5v64.1c0,3.09-.53,7.15.9,9.99,2.44,4.86,8.08,4.16,12.61,4.16h20.1c12.95,0,25.91.11,38.86,0,6.23-.06,10-4.32,11.89-10.09,1.09-3.34.55-7.51.55-10.96v-60.67c0-3.26-2.27-4.39-4.6-6.72l-8.08-8.08c-1.98-1.98-4-4.76-6.32-6.32-2.2-1.48-6.26-.64-8.93-.64h-45.71c-1.37,0-2.5,5.32-3.07,5.32h0Z'/%3e%3cpath%20class='st0'%20d='M117.73,16.41v19.64l.02.14h19.64c1.37,0,2.5-5.32,3.07-5.32h-16.27c-.41,0-3.08.29-3.34.05-.25-.23,0-2.54,0-2.99V11.37c0,.81-3.1,3.35-3.1,5.04h-.02Z'/%3e%3cpath%20class='st0'%20d='M70.28,47.64h39.27c1.37,0,2.5-5.32,3.07-5.32h-39.27c-1.37,0-2.5,5.32-3.07,5.32Z'/%3e%3cpath%20class='st0'%20d='M70.28,59.09h27.82c1.37,0,2.5-5.32,3.07-5.32h-27.82c-1.37,0-2.5,5.32-3.07,5.32Z'/%3e%3cpath%20class='st0'%20d='M71.92,75.46h46.5c3.58,0,7.31-.52,7.49,4.25.11,3.3,0,6.62,0,9.92,0,1.82.81,5.87-.08,7.59l2.41-3.81c-2.35,2.35-7.94,1.28-10.91,1.28h-37.62c-3.52,0-7.78.74-7.97-4.06-.13-3.35,0-6.75,0-10.1,0-1.9-.82-5.83.08-7.59l-2.41,3.81c.61-.82,1.44-1.24,2.51-1.28,1.55-.25,2.21-5.18,3.07-5.32-6.41,1.03-6.36,9.78-6.36,14.63,0,3.89-2.07,14.5,3.44,15.23,4.29.57,9.05,0,13.36,0h22.95c4.57,0,9.49.53,14.04,0,5.17-.61,6.57-7.44,6.57-11.74v-11.09c0-2.36.58-5.85-2.26-6.86-1.15-.41-2.76-.16-3.94-.16h-47.82c-1.37,0-2.5,5.32-3.07,5.32l.02-.02Z'/%3e%3cpath%20class='st1'%20d='M81.64,90.8c3.16,0,5.73-2.56,5.73-5.73s-2.56-5.73-5.73-5.73-5.73,2.56-5.73,5.73,2.56,5.73,5.73,5.73Z'/%3e%3cpath%20class='st0'%20d='M93.19,87.73h19.64c1.37,0,2.5-5.32,3.07-5.32h-19.64c-1.37,0-2.5,5.32-3.07,5.32Z'/%3e%3c/svg%3e)
%20--%3e%3cdefs%3e%3cstyle%3e%20.st0%20{%20fill:%20%23111;%20}%20.st1%20{%20fill:%20%23f0c53f;%20}%20.st2%20{%20fill:%20none;%20stroke:%20%23111;%20stroke-linecap:%20round;%20stroke-linejoin:%20round;%20stroke-width:%204px;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st0'%20d='M28.12,26.25h46.33c2.17,0,4.51-.46,6.28.61,1.93,1.17,3.7,3.7,5.29,5.29l7.04,7.04c2.44,2.44,3.03,2.4,3.03,5.56v63.33l3.77-6.33H35.6c-.66,0-2.84.39-3.43,0-.48-.32.07.15-.29-.83-1.07-2.89,0-8.21,0-11.26V19.92c0,.99-3.79,4.1-3.79,6.16v82l.02.17h68c1.04,0,3.77-5.36,3.77-6.33v-61.39c0-1.82.37-3.77-.5-5.26-1.01-1.73-3.35-3.35-4.75-4.75l-7.43-7.43c-2.54-2.54-2.77-3.34-6.15-3.34H31.88c-1.67,0-3.05,6.5-3.75,6.5,0,0-.01,0,0,0Z'/%3e%3cpath%20class='st0'%20d='M80.11,26.08v16l.02.17h16c.73,0,1.89-2.52,2.2-3.06.15-.26,1.62-3.44,1.55-3.44h-13.26c-.33,0-2.55.21-2.71.07-.15-.13,0-2.01,0-2.4v-13.5c0-.49-1.59,1.85-1.71,2.04-.63,1.02-2.08,2.84-2.08,4.13h-.01,0Z'/%3e%3cpath%20class='st0'%20d='M44.12,60.25h36c1.67,0,3.05-6.5,3.75-6.5h-36c-1.67,0-3.05,6.5-3.75,6.5Z'/%3e%3cpath%20class='st0'%20d='M44.12,74.25h26c1.67,0,3.05-6.5,3.75-6.5h-26c-1.67,0-3.05,6.5-3.75,6.5Z'/%3e%3cpath%20class='st0'%20d='M96.12,66.25h28c1.67,0,3.05-6.5,3.75-6.5h-28c-1.67,0-3.05,6.5-3.75,6.5Z'/%3e%3cpath%20class='st0'%20d='M138.12,40.25c11.67.3,22.08,7.83,25.13,19.3,1.85,6.94,1.1,15.07-4.56,19.97-4.64,4.01-10.68,6.25-16.82,6.23-11.64-.03-22.13-8.03-25.13-19.3-1.85-6.94-1.1-15.07,4.56-19.97,4.73-4.1,10.62-6.07,16.82-6.23,1.71-.04,2.99-6.48,3.75-6.5-23.02.6-39.28,31.99-23.02,49.94,8.59,9.48,23.19,11.21,33.82,4.13,8.18-5.45,14.67-16.71,15.18-26.53.79-15.01-11.2-27.16-25.98-27.55-1.62-.04-3.11,6.51-3.75,6.5h0Z'/%3e%3cpath%20class='st1'%20d='M140,77c7.73,0,14-6.27,14-14s-6.27-14-14-14-14,6.27-14,14,6.27,14,14,14Z'/%3e%3cpath%20class='st2'%20d='M133,63l5,5,10-11'/%3e%3cpath%20class='st0'%20d='M156.12,84.25l14,14c-.06-.06,4.57-5.67,3.75-6.5l-14-14c.06.06-4.57,5.67-3.75,6.5Z'/%3e%3c/svg%3e)
Request
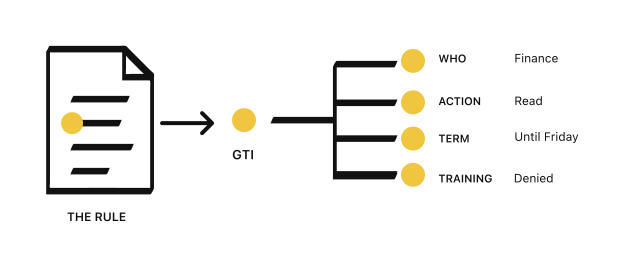
Who is asking, and for what purpose?
Check
Do the current conditions permit this action?
Use
The permitted object or connection is available within its terms.
Expiry
Access ends when the permitted time or purpose ends.
ONE also protects identity, policy, and intent.
ONE documents its constructions, comparative methodology and public figures through technical papers and source-backed research. Detailed specifications and security reductions are available under NDA.
%20--%3e%3cdefs%3e%3cstyle%3e%20.st0%20{%20fill:%20%23111;%20}%20.st1%20{%20fill:%20%23f0c53f;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st0'%20d='M64.23,15.82h48.39c3.26,0,4.99,3.17,7.23,5.41l7.42,7.42c.71.71,2.68,2.25,2.94,2.95.27.73,0,2.12,0,2.88v65.04c0,2.54.42,5.48,0,7.99-.59,3.55-7.45,2.64-10.31,2.64h-18.56c-11.3,0-22.63.25-33.93,0-5.07-.11-7.56-3.63-7.64-8.36-.06-3.92,0-7.86,0-11.78,0-23.61-.41-47.24,0-70.84.04-2.55,1.84-3.17,4.47-3.34,1.27-.09,2.08-4.62,2.69-4.66-5.86.38-9.78,7.04-9.88,12.49-.06,3.84,0,7.68,0,11.52v43.78c0,9.45-.46,19.02,0,28.46.29,6,4.93,7.4,9.91,7.4h17.84c12.47,0,24.97.19,37.44,0,5.89-.09,10.37-6.02,10.68-11.72.16-2.96,0-5.97,0-8.94v-61.26c0-1.99.6-4.82-.51-6.45-1.53-2.25-4.22-4.22-6.14-6.14-2.49-2.49-4.98-4.98-7.47-7.47-.88-.88-1.23-1.44-2.32-1.68-1.67-.37-3.83,0-5.53,0h-44.04c-1.2,0-2.19,4.66-2.69,4.66h0Z'/%3e%3cpath%20class='st0'%20d='M114.44,15.7v15.9h15.79c1.2,0,2.19-4.66,2.69-4.66h-13.08c-.32,0-2.47.23-2.68.04-.19-.18,0-2.02,0-2.4v-13.31c0-.35-1.14,1.33-1.23,1.46-.45.72-1.49,2.04-1.49,2.96h0Z'/%3e%3cpath%20class='st0'%20d='M71.41,44.52h43.04c1.2,0,2.19-4.66,2.69-4.66h-43.04c-1.2,0-2.19,4.66-2.69,4.66Z'/%3e%3cpath%20class='st0'%20d='M78.58,63.17c2.37.13,4.45,1.38,5.34,3.64.29.73.41,1.49.37,2.29-.11,2.3.19-.7.72-.55.16.05-2.21,1.23-1.92,1.14-.57.19-1.21.29-1.81.29-2.22,0-4.31-1.35-5.23-3.37-.32-.7-.49-1.48-.49-2.25,0-.32.02-.62.09-.93.17-.85-.09-.46-.78,1.16.14.02,1.86-1.12,1.92-1.14.59-.2,1.2-.26,1.81-.29.55-.03,1.34-1.78,1.58-2.19.11-.19,1.13-2.47,1.11-2.47-4.12.22-6.46,4.16-7.85,7.64-1.54,3.85.65,8.48,5.16,8.49,4.03.01,6.39-4.2,7.77-7.45,1.71-4.04-.49-8.44-5.08-8.69-1.12-.06-2.28,4.68-2.69,4.66h0l-.02.02Z'/%3e%3cpath%20class='st0'%20d='M110.14,63.17c2.37.13,4.45,1.38,5.34,3.64.29.73.41,1.49.37,2.29-.11,2.3.19-.7.72-.55.16.05-2.21,1.23-1.92,1.14-.57.19-1.21.29-1.81.29-2.22,0-4.31-1.35-5.23-3.37-.32-.7-.49-1.48-.49-2.25,0-.32.02-.62.09-.93.17-.85-.09-.46-.78,1.16.14.02,1.86-1.12,1.92-1.14.59-.2,1.2-.26,1.81-.29.55-.03,1.34-1.78,1.58-2.19.11-.19,1.13-2.47,1.11-2.47-4.12.22-6.46,4.16-7.85,7.64-1.54,3.85.65,8.48,5.16,8.49,4.03.01,6.39-4.2,7.77-7.45,1.71-4.04-.49-8.44-5.08-8.69-1.12-.06-2.28,4.68-2.69,4.66h0l-.02.02Z'/%3e%3cpath%20class='st0'%20d='M84.32,71.77c2.39,5.26,4.78,10.52,7.17,15.78-.28-.61,3.23-3.46,2.69-4.66-2.39-5.26-4.78-10.52-7.17-15.78.28.61-3.23,3.46-2.69,4.66Z'/%3e%3cpath%20class='st0'%20d='M104.63,70.99c-2.39,5.26-4.78,10.52-7.17,15.78-.44.96-.22.68.33.19.82-.75,1.44-2.29,1.9-3.29,2.39-5.26,4.78-10.52,7.17-15.78.44-.96.22-.68-.33-.19-.82.75-1.44,2.29-1.9,3.29Z'/%3e%3cpath%20class='st0'%20d='M71.41,106.2h43.04c1.2,0,2.19-4.66,2.69-4.66h-43.04c-1.2,0-2.19,4.66-2.69,4.66Z'/%3e%3cpath%20class='st1'%20d='M95.71,98.13c3.96,0,7.17-3.21,7.17-7.17s-3.21-7.17-7.17-7.17-7.17,3.21-7.17,7.17,3.21,7.17,7.17,7.17Z'/%3e%3c/svg%3e)
Papers
How the constructions and their security assumptions work.
%20--%3e%3cdefs%3e%3cstyle%3e%20.st0%20{%20fill:%20%23111;%20}%20.st1%20{%20fill:%20%23f0c53f;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st0'%20d='M39.42,114.23h110.03c1.39,0,2.54-5.42,3.13-5.42H42.55c-1.39,0-2.54,5.42-3.13,5.42h0Z'/%3e%3cpath%20class='st0'%20d='M50.9,98.95v-48.34l-3.14,5.28h26.25c.91,0,4.64-.6,5.35,0,.18.15.06,2.34.06,2.99v45.21c0-.83,3.16-3.42,3.16-5.13v-48.34l-.02-.14h-31.67c-.87,0-3.14,4.47-3.14,5.28v48.34c0-.83,3.16-3.42,3.16-5.13v-.02Z'/%3e%3cpath%20class='st0'%20d='M112.58,98.95V33.93l-3.14,5.28h20.36c3.3,0,6.88-.4,10.16,0,1.49.18,1.13-.16,1.13,1.63v63.25c0-.83,3.16-3.42,3.16-5.13V33.93l-.02-.14h-31.67c-.87,0-3.14,4.47-3.14,5.28v65.02c0-.83,3.16-3.42,3.16-5.13h0Z'/%3e%3cpath%20class='st0'%20d='M56.09,69.22h15c1.39,0,2.54-5.42,3.13-5.42h-15c-1.39,0-2.54,5.42-3.13,5.42Z'/%3e%3cpath%20class='st0'%20d='M117.77,52.55h15c1.39,0,2.54-5.42,3.13-5.42h-15c-1.39,0-2.54,5.42-3.13,5.42Z'/%3e%3cpath%20class='st0'%20d='M63.59,25.87h61.68c1.39,0,2.54-5.42,3.13-5.42h-61.67c-1.39,0-2.54,5.42-3.13,5.42h-.01Z'/%3e%3cpath%20class='st0'%20d='M63.58,19.06v13.34c0,.41,1.33-1.54,1.43-1.7.53-.85,1.73-2.37,1.73-3.44v-13.34c0-.41-1.33,1.54-1.43,1.7-.53.85-1.73,2.37-1.73,3.44Z'/%3e%3cpath%20class='st0'%20d='M125.26,19.06v13.34c0,.41,1.33-1.54,1.43-1.7.53-.85,1.73-2.37,1.73-3.44v-13.34c0-.41-1.33,1.54-1.43,1.7-.53.85-1.73,2.37-1.73,3.44Z'/%3e%3cpath%20class='st1'%20d='M96,30.67c4.14,0,7.5-3.36,7.5-7.5s-3.36-7.5-7.5-7.5-7.5,3.36-7.5,7.5,3.36,7.5,7.5,7.5Z'/%3e%3c/svg%3e)
Methodology
How comparisons are measured at matched security.
%20--%3e%3cdefs%3e%3cstyle%3e%20.st0%20{%20fill:%20%23111;%20}%20.st1%20{%20fill:%20%23f0c53f;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st0'%20d='M49.47,16.16h90.14c2.09,0,1.92-.39,1.92,1.79v29.82l2.99-5.02H54.38c-2.09,0-1.92.39-1.92-1.79V11.13c0,.79-3.01,3.25-3.01,4.89v31.75l.02.13h92.08c.83,0,2.99-4.25,2.99-5.02V11.13l-.02-.13H52.45c-1.33,0-2.42,5.16-2.98,5.16h0Z'/%3e%3cpath%20class='st0'%20d='M60.58,28.86h47.63c1.33,0,2.42-5.16,2.98-5.16h-47.63c-1.33,0-2.42,5.16-2.98,5.16Z'/%3e%3cpath%20class='st0'%20d='M60.58,38.39h34.93c1.33,0,2.42-5.16,2.98-5.16h-34.93c-1.33,0-2.42,5.16-2.98,5.16Z'/%3e%3cpath%20class='st1'%20d='M127.16,35.81c3.51,0,6.35-2.84,6.35-6.35s-2.84-6.35-6.35-6.35-6.35,2.84-6.35,6.35,2.84,6.35,6.35,6.35Z'/%3e%3cpath%20class='st0'%20d='M95.5,47.78v19.05c0-.79,3.01-3.25,3.01-4.89v-19.05c0,.79-3.01,3.25-3.01,4.89Z'/%3e%3cpath%20class='st0'%20d='M98.49,61.8h-31.75c-1.33,0-2.42,5.16-2.98,5.16h31.75c1.33,0,2.42-5.16,2.98-5.16Z'/%3e%3cpath%20class='st0'%20d='M95.51,66.96h31.75c1.33,0,2.42-5.16,2.98-5.16h-31.75c-1.33,0-2.42,5.16-2.98,5.16Z'/%3e%3cpath%20class='st0'%20d='M63.75,66.83v12.7c0,.39,1.26-1.47,1.36-1.62.5-.81,1.65-2.25,1.65-3.28v-12.7c0-.39-1.26,1.47-1.36,1.62-.5.81-1.65,2.25-1.65,3.28Z'/%3e%3cpath%20class='st0'%20d='M127.25,66.83v12.7c0,.39,1.26-1.47,1.36-1.62.5-.81,1.65-2.25,1.65-3.28v-12.7c0-.39-1.26,1.47-1.36,1.62-.5.81-1.65,2.25-1.65,3.28Z'/%3e%3cpath%20class='st0'%20d='M41.53,79.66h41.59c.45,0,2.75-.14,2.85-.03.6.65,0,4.73,0,5.56v27.67l2.99-5.02h-41.59c-.45,0-2.75.14-2.85.03-.6-.65,0-4.73,0-5.56v-27.67c0,.79-3.01,3.25-3.01,4.89v33.34l.02.13h44.45c.83,0,2.99-4.25,2.99-5.02v-33.34l-.02-.13h-44.44c-1.33,0-2.42,5.16-2.98,5.16h0Z'/%3e%3cpath%20class='st0'%20d='M105.03,79.66h41.59c.45,0,2.75-.14,2.85-.03.6.65,0,4.73,0,5.56v27.67l2.99-5.02h-41.59c-.45,0-2.75.14-2.85.03-.6-.65,0-4.73,0-5.56v-27.67c0,.79-3.01,3.25-3.01,4.89v33.34l.02.13h44.45c.83,0,2.99-4.25,2.99-5.02v-33.34l-.02-.13h-44.45c-1.33,0-2.42,5.16-2.98,5.16h0Z'/%3e%3cpath%20class='st0'%20d='M51.05,90.77h25.4c1.33,0,2.42-5.16,2.98-5.16h-25.4c-1.33,0-2.42,5.16-2.98,5.16Z'/%3e%3cpath%20class='st0'%20d='M51.05,100.3h17.46c1.33,0,2.42-5.16,2.98-5.16h-17.46c-1.33,0-2.42,5.16-2.98,5.16Z'/%3e%3cpath%20class='st0'%20d='M114.56,90.77h25.4c1.33,0,2.42-5.16,2.98-5.16h-25.4c-1.33,0-2.42,5.16-2.98,5.16h0Z'/%3e%3cpath%20class='st0'%20d='M114.56,100.3h17.46c1.33,0,2.42-5.16,2.98-5.16h-17.46c-1.33,0-2.42,5.16-2.98,5.16h0Z'/%3e%3c/svg%3e)
Sources
Where public figures and supporting research come from.