ONE makes digital connections programmable by binding identity, purpose, policy, and encryption inside the handshake.
- Programmable handshake
- Object semantic cipher
- Context-aware KEM
Programmable handshake
The connection checks who is acting and what they are allowed to do before it opens.
Object semantic cipher
The owner's terms travel inside an encrypted object.
Context-aware KEM
Post-quantum key exchange binds context to the cryptographic relationship.
Plain-language policy
State a rule in a sentence. GTI compiles it into enforceable conditions.
Identity is verified. Policy is embedded. Trust travels inside the connection - not the perimeter.
%20--%3e%3cdefs%3e%3cstyle%3e%20.st0%20{%20fill:%20%23111;%20}%20.st1%20{%20fill:%20%23f0c53f;%20}%20.st2%20{%20fill:%20none;%20stroke:%20%23111;%20stroke-linecap:%20round;%20stroke-linejoin:%20round;%20stroke-width:%205px;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st0'%20d='M66.26,19.87h38c1.08,0,2.96-.38,4,0,.91.33,1.87,1.74,2.55,2.43,2.24,2.24,4.47,4.47,6.71,6.71,1.74,1.74,3.82,3.41,5.35,5.35.55.69.36.07.45,1.22.26,3.54,0,7.2,0,10.76v54.63c0,2.22-.37,4.82,0,7.03l-.06.94,1.18-2.02c1.58-2.03,1.73-2.55.46-1.54-1.2.33-1.98.76-3.25.83-.24.01-.5,0-.74,0-1.61.03-3.23,0-4.84,0h-36.71c-3.06,0-6.79.56-9.81-.24-4.66-1.24-4.95-5.5-4.95-9.4v-12.86c0-21.66-.42-43.36,0-65.02,0-.18.03-.39,0-.57-.63-3.78-1.37,4.16-2.3,3.1-.28-.32,3.4-1.27,3.97-1.31,1.05-.07,2.53-3.36,2.99-4.16.22-.37,2.12-4.67,2.11-4.67-5.32.35-7.92,5.5-10.1,9.76-1.03,2.02-1.78,3.95-1.82,6.22-.07,3.39,0,6.78,0,10.17v39.77c0,9.99-.1,19.98,0,29.96.05,4.6,2.49,7.96,7.39,8.06,4.56.09,9.13,0,13.68,0,11.72,0,23.46.19,35.18,0,2.32-.04,4.34-.55,6.05-2.25,3.11-3.09,6.45-8.68,6.71-13.15.14-2.54,0-5.13,0-7.67V28.75c0-.68.22-1.83,0-2.48-.38-1.13-1.98-2.22-2.83-3.06l-7.03-7.03c-1.35-1.35-3.24-4.17-5-5-.67-.32-1.77-.13-2.53-.13h-39.72c-.99,0-2.57,3.42-2.99,4.16-.2.35-2.2,4.67-2.11,4.67h.01,0Z'/%3e%3cpath%20class='st0'%20d='M109.65,17.55v15.06h14.96c1.13,0,2.07-4.42,2.55-4.42h-12.39c-.31,0-2.34.22-2.54.04-.18-.17,0-1.92,0-2.27v-12.61c0-.33-1.08,1.26-1.16,1.39-.43.69-1.41,1.94-1.41,2.81h0Z'/%3e%3cpath%20class='st1'%20d='M76.96,54.32c2.7,0,4.89-2.19,4.89-4.89s-2.19-4.89-4.89-4.89-4.89,2.19-4.89,4.89,2.19,4.89,4.89,4.89Z'/%3e%3cpath%20class='st0'%20d='M89.27,51.63h21.74c1.13,0,2.07-4.42,2.55-4.42h-21.74c-1.13,0-2.07,4.42-2.55,4.42Z'/%3e%3cpath%20class='st1'%20d='M76.96,71.98c2.7,0,4.89-2.19,4.89-4.89s-2.19-4.89-4.89-4.89-4.89,2.19-4.89,4.89,2.19,4.89,4.89,4.89Z'/%3e%3cpath%20class='st0'%20d='M89.27,69.3h21.74c1.13,0,2.07-4.42,2.55-4.42h-21.74c-1.13,0-2.07,4.42-2.55,4.42Z'/%3e%3cpath%20class='st1'%20d='M76.96,89.65c2.7,0,4.89-2.19,4.89-4.89s-2.19-4.89-4.89-4.89-4.89,2.19-4.89,4.89,2.19,4.89,4.89,4.89Z'/%3e%3cpath%20class='st0'%20d='M89.27,86.97h14.95c1.13,0,2.07-4.42,2.55-4.42h-14.95c-1.13,0-2.07,4.42-2.55,4.42Z'/%3e%3cpath%20class='st1'%20d='M128.75,87.48c6.75,0,12.23-5.48,12.23-12.23s-5.48-12.23-12.23-12.23-12.23,5.48-12.23,12.23,5.48,12.23,12.23,12.23Z'/%3e%3cpath%20class='st2'%20d='M122.64,75.25l4.76,4.76,8.15-9.51'/%3e%3c/svg%3e)
State who may connect, for what purpose, on which device and for how long.
%20--%3e%3cdefs%3e%3cstyle%3e%20.st0,%20.st1%20{%20fill:%20%23111;%20}%20.st2%20{%20fill:%20%23f0c53f;%20}%20.st1%20{%20stroke:%20%23212020;%20stroke-miterlimit:%208;%20stroke-width:%204px;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st0'%20d='M26.12,36.25h19.96c4.85,0,15.28-2.22,16.02,4.48.78,7.09,0,14.71,0,21.85v12.34c0,1.41.61,4.55-.1,5.93l2.95-4.66c-2.25,2.25-5.92,1.57-8.85,1.57h-13.21c-4.64,0-16.22,2.3-17-4.23-.83-6.99,0-14.56,0-21.6v-12.49c0-1.49-.64-4.83.1-6.27l-2.95,4.66c.74-1,1.76-1.52,3.07-1.57,1.9-.31,2.7-6.33,3.75-6.5-5.41.87-7.77,8.2-7.77,13.03v21.77c0,5.03-.64,10.54,0,15.53.8,6.27,11.12,4.17,15.57,4.17,6.54,0,13.44.65,19.95,0,4.89-.49,8.09-6.9,8.26-11.45.26-6.77,0-13.6,0-20.38,0-5.94.55-12.18,0-18.1-.62-6.64-10.33-4.57-15.09-4.57h-20.93c-1.67,0-3.05,6.5-3.75,6.5h.02,0Z'/%3e%3cpath%20class='st0'%20d='M34.12,50.25h16c.73,0,1.89-2.52,2.2-3.06.15-.26,1.62-3.44,1.55-3.44h-16c-.73,0-1.89,2.52-2.2,3.06-.15.26-1.62,3.44-1.55,3.44Z'/%3e%3cpath%20class='st0'%20d='M34.12,62.25h12c.73,0,1.89-2.52,2.2-3.06.15-.26,1.62-3.44,1.55-3.44h-12c-.73,0-1.89,2.52-2.2,3.06-.15.26-1.62,3.44-1.55,3.44Z'/%3e%3cpath%20class='st0'%20d='M130.12,36.25h19.96c4.85,0,15.28-2.22,16.02,4.48.78,7.09,0,14.71,0,21.85v12.34c0,1.41.61,4.55-.1,5.93l2.95-4.66c-2.25,2.25-5.92,1.57-8.85,1.57h-13.21c-4.64,0-16.22,2.3-17-4.23-.83-6.99,0-14.56,0-21.6v-12.49c0-1.49-.64-4.83.1-6.27l-2.95,4.66c.74-1,1.76-1.52,3.07-1.57,1.9-.31,2.7-6.33,3.75-6.5-5.41.87-7.77,8.2-7.77,13.03v21.77c0,5.03-.64,10.54,0,15.53.8,6.27,11.12,4.17,15.57,4.17,6.54,0,13.44.65,19.95,0,4.89-.49,8.09-6.9,8.26-11.45.26-6.77,0-13.6,0-20.38,0-5.94.55-12.18,0-18.1-.62-6.64-10.33-4.57-15.09-4.57h-20.93c-1.67,0-3.05,6.5-3.75,6.5h.02Z'/%3e%3cpath%20class='st0'%20d='M138.12,50.25h16c.73,0,1.89-2.52,2.2-3.06.15-.26,1.62-3.44,1.55-3.44h-16c-.73,0-1.89,2.52-2.2,3.06-.15.26-1.62,3.44-1.55,3.44Z'/%3e%3cpath%20class='st0'%20d='M138.12,62.25h12c.73,0,1.89-2.52,2.2-3.06.15-.26,1.62-3.44,1.55-3.44h-12c-.73,0-1.89,2.52-2.2,3.06-.15.26-1.62,3.44-1.55,3.44Z'/%3e%3cpath%20class='st0'%20d='M62.12,60.25h18c1.67,0,3.05-6.5,3.75-6.5h-18c-1.67,0-3.05,6.5-3.75,6.5Z'/%3e%3cpath%20class='st0'%20d='M108.12,60.25h18c1.67,0,3.05-6.5,3.75-6.5h-18c-1.67,0-3.05,6.5-3.75,6.5Z'/%3e%3cpath%20class='st0'%20d='M94.11,74.08v24c0-.99,3.79-4.1,3.79-6.16v-24c0,.99-3.79,4.1-3.79,6.16Z'/%3e%3cpath%20class='st0'%20d='M70.12,98.25h48c1.67,0,3.05-6.5,3.75-6.5h-48c-1.67,0-3.05,6.5-3.75,6.5Z'/%3e%3cpath%20class='st1'%20d='M74,99c2.21,0,4-1.79,4-4s-1.79-4-4-4-4,1.79-4,4,1.79,4,4,4Z'/%3e%3cpath%20class='st1'%20d='M96,99c2.21,0,4-1.79,4-4s-1.79-4-4-4-4,1.79-4,4,1.79,4,4,4Z'/%3e%3cpath%20class='st1'%20d='M118,99c2.21,0,4-1.79,4-4s-1.79-4-4-4-4,1.79-4,4,1.79,4,4,4Z'/%3e%3cpath%20class='st2'%20d='M96,71c7.73,0,14-6.27,14-14s-6.27-14-14-14-14,6.27-14,14,6.27,14,14,14Z'/%3e%3c/svg%3e)
Each clause becomes a condition the connection must satisfy.
%20--%3e%3cdefs%3e%3cstyle%3e%20.st0%20{%20fill:%20%23111;%20}%20.st1%20{%20fill:%20%23f0c53f;%20}%20.st2%20{%20stroke-width:%204px;%20}%20.st2,%20.st3%20{%20fill:%20none;%20stroke:%20%23111;%20stroke-linecap:%20round;%20stroke-linejoin:%20round;%20}%20.st3%20{%20stroke-width:%205px;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st2'%20d='M28.85,63h36.22M52.99,75.07l12.07-12.07-12.07-12.07'/%3e%3cpath%20class='st0'%20d='M80.56,27.21h25.03c1.03,0,7.55-.37,7.71-.18.58.72,0,4.21,0,5.1v77.58c2.16-3.64,4.34-7.28,6.5-10.92h-23.5c-7.99,0-19.02.99-19.58-10.17-.81-16.08,0-32.4,0-48.5v-11.36c0-.69-.03-1.38,0-2.07,0-.16.03-.82.03-.62,0-.56.08-1.1.21-1.65-3.71,5.01-4.59,6.67-2.64,5,2.29-.77,3.59-2.08,6.25-2.22,1.32-.07,3.22-4.29,3.79-5.28.28-.47,2.71-5.92,2.67-5.92-8.2.45-12.7,9.15-15.54,15.88-1.21,2.88-1.31,5.43-1.31,8.43v56.54c0,3.16.05,6.16,2.04,8.87,2.9,3.95,7.12,4.24,11.54,4.24h29.58c1.8,0,6.5-9.24,6.5-10.92V16.29l-.03-.28h-32.77c-1.26,0-3.26,4.35-3.79,5.28-.26.45-2.79,5.92-2.67,5.92h-.02Z'/%3e%3cpath%20class='st1'%20d='M95.86,78.52c8.57,0,15.52-6.95,15.52-15.52s-6.95-15.52-15.52-15.52-15.52,6.95-15.52,15.52,6.95,15.52,15.52,15.52Z'/%3e%3cpath%20class='st3'%20d='M88.1,63l6.04,6.04,10.35-12.07'/%3e%3cpath%20class='st2'%20d='M124.93,63h36.22M149.08,75.07l12.07-12.07-12.07-12.07'/%3e%3c/svg%3e)
If a condition fails, the connection does not receive a key.
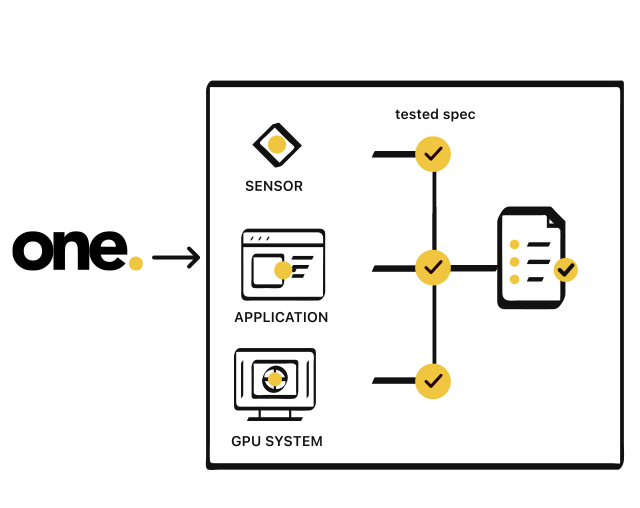
A sensor, a business application and a GPU cluster do not have the same constraints. ONE configures the cryptography for each environment, then tests and releases that configuration as a signed version.
%20--%3e%3cdefs%3e%3cstyle%3e%20.st0%20{%20fill:%20%23111;%20}%20.st1%20{%20fill:%20%23f0c53f;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st0'%20d='M39.89,32.92c.21-4.83,2.36-7.13,6.94-8.77,2.97-1.06,6.27-1.19,9.32-.39,6.86,1.8,11.94,8.19,11.95,15.32,0,3.93-1.38,5.94-4.7,7.76-3.5,1.92-7.7,2.4-11.56,1.4-7.05-1.85-11.65-8.16-11.95-15.32.04.92-3.88,4.14-3.79,6.16.48,11.29,11.68,19.61,22.53,14.77,7.15-3.19,13.24-13.14,13.26-20.94.02-11.44-12.03-19.42-22.53-14.77-7.38,3.26-12.92,13.07-13.26,20.94.05-1.05,3.7-4.07,3.79-6.16Z'/%3e%3cpath%20class='st0'%20d='M54,40c2.21,0,4-1.79,4-4s-1.79-4-4-4-4,1.79-4,4,1.79,4,4,4Z'/%3e%3cpath%20class='st0'%20d='M68.12,39.25h84.43c.47,0,3.3-.3,3.55-.06.63.62,0,5.5,0,6.39v5.5l3.77-6.33c-3.03,0-8.06,1.04-10.8,0-1.55-.59-1.18-.1-1.18-2.38v-5.46c0,.99-3.79,4.1-3.79,6.16v8l.02.17h12c1.04,0,3.77-5.36,3.77-6.33v-12l-.02-.17h-88c-1.67,0-3.05,6.5-3.75,6.5h0Z'/%3e%3cpath%20class='st0'%20d='M130.11,39.08v12c0,.49,1.59-1.85,1.71-2.04.63-1.02,2.08-2.84,2.08-4.13v-12c0-.49-1.59,1.85-1.71,2.04-.63,1.02-2.08,2.84-2.08,4.13Z'/%3e%3cpath%20class='st0'%20d='M39.89,86.92c.21-4.83,2.36-7.13,6.94-8.77,2.97-1.06,6.27-1.19,9.32-.39,6.86,1.8,11.94,8.19,11.95,15.32,0,3.93-1.38,5.94-4.7,7.76-3.5,1.92-7.7,2.4-11.56,1.4-7.05-1.85-11.65-8.16-11.95-15.32.04.92-3.88,4.14-3.79,6.16.48,11.29,11.68,19.61,22.53,14.77,7.15-3.19,13.24-13.14,13.26-20.94.02-11.44-12.03-19.42-22.53-14.77-7.38,3.26-12.92,13.07-13.26,20.94.05-1.05,3.7-4.07,3.79-6.16Z'/%3e%3cpath%20class='st1'%20d='M54,94c2.21,0,4-1.79,4-4s-1.79-4-4-4-4,1.79-4,4,1.79,4,4,4Z'/%3e%3cpath%20class='st0'%20d='M68.12,93.25h40.08c1.17,0,4.19-.57,5.24,0,1.76.96.67,9.16.67,11.83l3.77-6.33c-3.03,0-8.06,1.04-10.8,0-1.55-.59-1.18-.1-1.18-2.38v-5.46c0,.99-3.79,4.1-3.79,6.16v8l.02.17h12c1.04,0,3.77-5.36,3.77-6.33v-12l-.02-.17h-46c-1.67,0-3.05,6.5-3.75,6.5h0Z'/%3e%3cpath%20class='st1'%20d='M134,98c4.42,0,8-3.58,8-8s-3.58-8-8-8-8,3.58-8,8,3.58,8,8,8Z'/%3e%3c/svg%3e)
%20--%3e%3cdefs%3e%3cstyle%3e%20.st0%20{%20fill:%20%23111;%20}%20.st1%20{%20fill:%20%23f0c53f;%20}%20.st2%20{%20fill:%20none;%20stroke:%20%23111;%20stroke-linecap:%20round;%20stroke-linejoin:%20round;%20stroke-width:%204px;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st0'%20d='M26.12,28.25h21.77c2.63,0,5.59-.38,8.21,0,3.46.51,3.94,2.82,4,5.67.36,16.6,0,33.25,0,49.85v11.82c0,1.3.54,4.01-.1,5.25l2.95-4.66c-2.3,2.3-6.15,1.57-9.14,1.57h-14.33c-5.19,0-13.42,1.83-13.59-5.33-.4-16.56,0-33.19,0-49.76v-12.25c0-1.29-.54-4.01.1-5.25l-2.95,4.66c.74-1,1.76-1.52,3.07-1.57,1.9-.31,2.7-6.33,3.75-6.5-6.77,1.09-7.77,9.82-7.77,15.37v56.76c0,1.97-.24,4.12,0,6.07.5,4,3.28,4.29,6.53,4.29,8.87,0,17.97.62,26.82,0,6.06-.42,8.44-8.11,8.44-13.36v-56.15c0-2.74.25-5.61,0-8.34-.36-3.94-2.88-4.64-6.25-4.64h-27.77c-1.67,0-3.05,6.5-3.75,6.5h.01Z'/%3e%3cpath%20class='st0'%20d='M34.12,44.25h14c.73,0,1.89-2.52,2.2-3.06.15-.26,1.62-3.44,1.55-3.44h-14c-.73,0-1.89,2.52-2.2,3.06-.15.26-1.62,3.44-1.55,3.44Z'/%3e%3cpath%20class='st0'%20d='M34.12,56.25h14c.73,0,1.89-2.52,2.2-3.06.15-.26,1.62-3.44,1.55-3.44h-14c-.73,0-1.89,2.52-2.2,3.06-.15.26-1.62,3.44-1.55,3.44Z'/%3e%3cpath%20class='st0'%20d='M132.12,28.25h21.77c2.63,0,5.59-.38,8.21,0,3.46.51,3.94,2.82,4,5.67.36,16.6,0,33.25,0,49.85v11.82c0,1.3.54,4.01-.1,5.25l2.95-4.66c-2.3,2.3-6.15,1.57-9.14,1.57h-14.33c-5.19,0-13.42,1.83-13.59-5.33-.4-16.56,0-33.19,0-49.76v-12.25c0-1.29-.54-4.01.1-5.25l-2.95,4.66c.74-1,1.76-1.52,3.07-1.57,1.9-.31,2.7-6.33,3.75-6.5-6.77,1.09-7.77,9.82-7.77,15.37v56.76c0,1.97-.24,4.12,0,6.07.5,4,3.28,4.29,6.53,4.29,8.87,0,17.97.62,26.82,0,6.06-.42,8.44-8.11,8.44-13.36v-56.15c0-2.74.25-5.61,0-8.34-.36-3.94-2.88-4.64-6.25-4.64h-27.77c-1.67,0-3.05,6.5-3.75,6.5h0Z'/%3e%3cpath%20class='st0'%20d='M140.12,44.25h14c.73,0,1.89-2.52,2.2-3.06.15-.26,1.62-3.44,1.55-3.44h-14c-.73,0-1.89,2.52-2.2,3.06-.15.26-1.62,3.44-1.55,3.44Z'/%3e%3cpath%20class='st0'%20d='M140.12,56.25h14c.73,0,1.89-2.52,2.2-3.06.15-.26,1.62-3.44,1.55-3.44h-14c-.73,0-1.89,2.52-2.2,3.06-.15.26-1.62,3.44-1.55,3.44Z'/%3e%3cpath%20class='st2'%20d='M117,83.92h-42M89,69.92l-14,14,14,14'/%3e%3cpath%20class='st2'%20d='M72,48.16h52M110,62.16l14-14-14-14'/%3e%3cpath%20class='st1'%20d='M96,57c5.52,0,10-4.48,10-10s-4.48-10-10-10-10,4.48-10,10,4.48,10,10,10Z'/%3e%3c/svg%3e)
%20--%3e%3cdefs%3e%3cstyle%3e%20.st0%20{%20fill:%20%23111;%20}%20.st1%20{%20fill:%20%23f0c53f;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st0'%20d='M32.12,32.25h54.96c2.24,0,4.79-.34,7.02,0,4.23.64,4,3.95,4,7.23v49.03c0,2.04.89,6.41-.1,8.33l2.95-4.66c-2.21,2.21-5.66,1.57-8.53,1.57h-48.49c-2.57,0-5.42.35-7.97,0-4.1-.57-4.07-3.56-4.07-6.75v-49.51c0-2.01-.89-6.41.1-8.33l-2.95,4.66c.74-1,1.76-1.52,3.07-1.57,1.9-.31,2.7-6.33,3.75-6.5-4.22.68-7.45,6.69-7.77,10.67-.27,3.34,0,6.83,0,10.18v37.35c0,3.77-.19,7.6,0,11.36.17,3.46,2.1,4.81,5.32,4.93,10.37.4,20.83,0,31.2,0,9.47,0,19.56,1.02,28.98,0,8.05-.87,8.29-11.06,8.29-17.22v-50.64c0-3.21-.12-6.09-4.21-6.64-3.48-.46-7.34,0-10.84,0h-50.97c-1.67,0-3.05,6.5-3.75,6.5h0Z'/%3e%3cpath%20class='st0'%20d='M46.12,54.25h34c1.67,0,3.05-6.5,3.75-6.5h-34c-1.67,0-3.05,6.5-3.75,6.5Z'/%3e%3cpath%20class='st0'%20d='M46.12,68.25h28c1.67,0,3.05-6.5,3.75-6.5h-28c-1.67,0-3.05,6.5-3.75,6.5Z'/%3e%3cpath%20class='st0'%20d='M46.12,82.25h20c1.67,0,3.05-6.5,3.75-6.5h-20c-1.67,0-3.05,6.5-3.75,6.5Z'/%3e%3cpath%20class='st0'%20d='M98.12,32.25h36.33c5.6,0,11.23-.15,16.83,0,6.03.16,8.68,4.1,8.83,9.75.35,14.09,0,28.23,0,42.33,0,2.19.04,4.38,0,6.57,0,.37-.04.78,0,1.16,0,.04-.09,1.27-.11,1.32.93-1.64.39-1.65-1.6-.03-.82.27-1.66.41-2.52.41-4.03.31-8.21,0-12.26,0h-41.74c-1.67,0-3.05,6.5-3.75,6.5h39.1c4.9,0,9.95.36,14.84,0,6.69-.49,11.47-8.51,11.83-14.73.82-14.01,0-28.3,0-42.33,0-4.39,1.13-11.02-1.97-14.63-3.44-4.01-10.33-2.82-15.06-2.82h-44.99c-1.67,0-3.05,6.5-3.75,6.5h-.01Z'/%3e%3cpath%20class='st1'%20d='M122,55.6c3.64,0,6.6-2.95,6.6-6.6s-2.96-6.6-6.6-6.6-6.6,2.95-6.6,6.6,2.96,6.6,6.6,6.6Z'/%3e%3cpath%20class='st1'%20d='M140,69.6c3.65,0,6.6-2.96,6.6-6.6s-2.96-6.6-6.6-6.6-6.6,2.95-6.6,6.6,2.96,6.6,6.6,6.6Z'/%3e%3cpath%20class='st1'%20d='M122,83.6c3.64,0,6.6-2.96,6.6-6.6s-2.96-6.6-6.6-6.6-6.6,2.96-6.6,6.6,2.96,6.6,6.6,6.6Z'/%3e%3c/svg%3e)
%20--%3e%3cdefs%3e%3cstyle%3e%20.st0%20{%20fill:%20%23111;%20}%20.st1%20{%20fill:%20%23f0c53f;%20}%20.st2%20{%20fill:%20none;%20stroke:%20%23111;%20stroke-linecap:%20round;%20stroke-linejoin:%20round;%20stroke-width:%204px;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st2'%20d='M60,63h77M123,77l14-14-14-14'/%3e%3cpath%20class='st0'%20d='M22.12,44.25h17.16c1.99,0,4.82-.47,6.65.49,2.43,1.28,2.17,3.71,2.17,6.01v29.46c0,1.14.46,3.53-.1,4.63l2.95-4.66c-2.13,2.13-5.15,1.57-7.91,1.57h-11.01c-1.96,0-4.21.31-6.16,0-3.55-.56-3.98-2.99-3.98-5.97v-29.99c0-1.12-.46-3.54.1-4.63l-2.95,4.66c.74-1,1.76-1.52,3.07-1.57,1.9-.31,2.7-6.33,3.75-6.5-4.54.73-7.59,7.16-7.77,11.38-.24,5.63,0,11.32,0,16.95s-.18,11.19,0,16.77c.16,5.22,3.73,5.4,8.04,5.4,5.74,0,11.76.54,17.47,0,4.57-.43,7.89-6.36,8.28-10.65.98-10.82,0-22.15,0-33.01,0-1.69.27-3.75-.79-5.19-1.61-2.19-4.88-1.64-7.24-1.64h-17.98c-1.67,0-3.05,6.5-3.75,6.5h0Z'/%3e%3cpath%20class='st0'%20d='M144.12,44.25h17.16c1.99,0,4.82-.47,6.65.49,2.43,1.28,2.17,3.71,2.17,6.01v29.46c0,1.14.46,3.53-.1,4.63l2.95-4.66c-2.13,2.13-5.15,1.57-7.91,1.57h-11.01c-1.96,0-4.21.31-6.16,0-3.55-.56-3.98-2.99-3.98-5.97v-29.99c0-1.12-.46-3.54.1-4.63l-2.95,4.66c.74-1,1.76-1.52,3.07-1.57,1.9-.31,2.7-6.33,3.75-6.5-4.54.73-7.59,7.16-7.77,11.38-.24,5.63,0,11.32,0,16.95s-.18,11.19,0,16.77c.16,5.22,3.73,5.4,8.04,5.4,5.74,0,11.76.54,17.47,0,4.57-.43,7.89-6.36,8.28-10.65.98-10.82,0-22.15,0-33.01,0-1.69.27-3.75-.79-5.19-1.61-2.19-4.88-1.64-7.24-1.64h-17.98c-1.67,0-3.05,6.5-3.75,6.5h0Z'/%3e%3cpath%20class='st1'%20d='M96,81c9.94,0,18-8.06,18-18s-8.06-18-18-18-18,8.06-18,18,8.06,18,18,18Z'/%3e%3cpath%20class='st2'%20d='M88,63l6,6,10-12'/%3e%3c/svg%3e)
A cryptographic foundation designed for AI and the quantum era, with post-quantum options available as part of the architecture.
Explore the Technology