Identity, purpose and policy become conditions of the
cryptographic handshake, so an action can be
governed before data moves.
ONE places identity, purpose, and policy inside the
connection itself. If its conditions are not met, the connection
does not open.
ONE lives inside the connection
How ONE works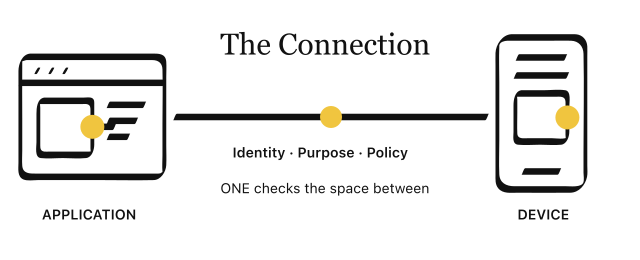
SDK: The kit
Select and implement cryptography for your environment.
GTI: The graph
Compile and govern the terms a connection must satisfy.
OZEO: The channel
Govern communication between people, systems and AI agents.
Vault: The object
Wrap a file with rules for who can use it, for what purpose and for how long. Those rules stay with the file when it moves.
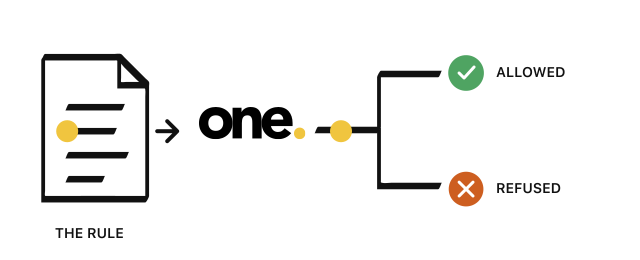
Identity, purpose, policy and context become conditions of the handshake. When a condition fails, the connection is refused before data moves.
%20--%3e%3cdefs%3e%3cstyle%3e%20.st0%20{%20fill:%20%23111;%20}%20.st1%20{%20fill:%20%23f0c53f;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st0'%20d='M42.23,107.85V29.78l-3.07,5.15h24.32c3.85,0,8.2-.57,12.01,0,1.55.24,1.06.24,1.06,2.23v75.71c0-.81,3.08-3.33,3.08-5.01V29.78l-.02-.14h-37.39c-.85,0-3.07,4.36-3.07,5.15v78.07c0-.81,3.08-3.33,3.08-5.01h0Z'/%3e%3cpath%20class='st0'%20d='M115.43,107.85V15.14l-3.07,5.15h28.42c1.22,0,8.38-.74,8.97-.1s0,4.53,0,5.33v87.35c0-.81,3.08-3.33,3.08-5.01V15.14l-.02-.14h-37.41c-.85,0-3.07,4.36-3.07,5.15v92.71c0-.81,3.08-3.33,3.08-5.01h.02Z'/%3e%3cpath%20class='st0'%20d='M32.66,113h123.62c1.36,0,2.48-5.29,3.05-5.29H35.72c-1.36,0-2.48,5.29-3.05,5.29h-.01Z'/%3e%3cpath%20class='st0'%20d='M48.93,49.56h14.64c1.36,0,2.48-5.29,3.05-5.29h-14.64c-1.36,0-2.48,5.29-3.05,5.29Z'/%3e%3cpath%20class='st0'%20d='M48.93,62.58h14.64c1.36,0,2.48-5.29,3.05-5.29h-14.64c-1.36,0-2.48,5.29-3.05,5.29Z'/%3e%3cpath%20class='st0'%20d='M48.93,75.59h14.64c1.36,0,2.48-5.29,3.05-5.29h-14.64c-1.36,0-2.48,5.29-3.05,5.29Z'/%3e%3cpath%20class='st0'%20d='M48.93,88.6h14.64c1.36,0,2.48-5.29,3.05-5.29h-14.64c-1.36,0-2.48,5.29-3.05,5.29Z'/%3e%3cpath%20class='st0'%20d='M122.12,36.55h16.27c1.36,0,2.48-5.29,3.05-5.29h-16.27c-1.36,0-2.48,5.29-3.05,5.29Z'/%3e%3cpath%20class='st0'%20d='M122.12,49.56h16.27c1.36,0,2.48-5.29,3.05-5.29h-16.27c-1.36,0-2.48,5.29-3.05,5.29Z'/%3e%3cpath%20class='st0'%20d='M122.12,62.58h16.27c1.36,0,2.48-5.29,3.05-5.29h-16.27c-1.36,0-2.48,5.29-3.05,5.29Z'/%3e%3cpath%20class='st0'%20d='M122.12,75.59h16.27c1.36,0,2.48-5.29,3.05-5.29h-16.27c-1.36,0-2.48,5.29-3.05,5.29Z'/%3e%3cpath%20class='st0'%20d='M122.12,88.6h16.27c1.36,0,2.48-5.29,3.05-5.29h-16.27c-1.36,0-2.48,5.29-3.05,5.29Z'/%3e%3cpath%20class='st0'%20d='M76.58,65.83h35.78c1.36,0,2.48-5.29,3.05-5.29h-35.78c-1.36,0-2.48,5.29-3.05,5.29Z'/%3e%3cpath%20class='st1'%20d='M96,72.95c5.39,0,9.76-4.37,9.76-9.76s-4.37-9.76-9.76-9.76-9.76,4.37-9.76,9.76,4.37,9.76,9.76,9.76Z'/%3e%3c/svg%3e)
Enterprise
Data moves. Identities sprawl. ONE binds identity, purpose and policy to the connection before a single byte moves.
View Solutions%20--%3e%3cdefs%3e%3cstyle%3e%20.st0,%20.st1%20{%20fill:%20%23111;%20}%20.st2%20{%20fill:%20%23f0c53f;%20}%20.st1%20{%20stroke:%20%23090909;%20stroke-miterlimit:%2010;%20stroke-width:%20.25px;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st0'%20d='M39.62,37.6h27.39c1.86,0,4.34-.36,6.11.39,4.54,1.92,3.03,10.16,3.03,14.02v23.39c0,4.51-.05,9.03,0,13.54,0,.06.78-1.05.81-1.05-.91.11-1.69.69-2.66.8-.12.02-.23,0-.35,0-.89.07-1.83,0-2.72,0h-10.23c-5.97,0-12.2.52-18.15,0-6.28-.55-5.08-7.3-5.08-11.81v-36.11c0-.73.27-2.08,0-2.77-.06-.15,0-.47,0-.63v-.05c-1.13,1.12-1.12,1.36.02.72.56-.33,1.17-.48,1.84-.45,1.52-.15,2.35-5.32,3.12-5.4-6.27.63-8.12,8.45-8.12,13.69v23.95c0,6.23-.39,12.6,0,18.82.45,7.12,8.91,5.42,13.93,5.42,7.34,0,14.85.47,22.19,0,5.55-.35,8.56-7.07,8.56-12.06,0-14.5.28-29.02,0-43.51-.15-7.79-7.92-6.31-13.56-6.31h-23.01c-1.39,0-2.53,5.4-3.12,5.4h0Z'/%3e%3cpath%20class='st1'%20d='M49.49,59.82c1.84,0,3.32-1.49,3.32-3.32s-1.49-3.32-3.32-3.32-3.32,1.49-3.32,3.32,1.49,3.32,3.32,3.32Z'/%3e%3cpath%20class='st1'%20d='M64.44,59.82c1.84,0,3.32-1.49,3.32-3.32s-1.49-3.32-3.32-3.32-3.32,1.49-3.32,3.32,1.49,3.32,3.32,3.32Z'/%3e%3cpath%20class='st0'%20d='M47.92,75.81h14.95c1.39,0,2.53-5.4,3.12-5.4h-14.95c-1.39,0-2.53,5.4-3.12,5.4Z'/%3e%3cpath%20class='st0'%20d='M76.17,65.84h36.55c1.39,0,2.53-5.4,3.12-5.4h-36.55c-1.39,0-2.53,5.4-3.12,5.4Z'/%3e%3cpath%20class='st2'%20d='M96.01,73.11c5.51,0,9.97-4.46,9.97-9.97s-4.46-9.97-9.97-9.97-9.97,4.46-9.97,9.97,4.46,9.97,9.97,9.97Z'/%3e%3cpath%20class='st0'%20d='M112.72,65.84h13.29c.61,0,1.57-2.09,1.83-2.54.12-.22,1.35-2.86,1.29-2.86h-13.29c-.61,0-1.57,2.09-1.83,2.54-.12.22-1.35,2.86-1.29,2.86Z'/%3e%3cpath%20class='st0'%20d='M129.14,60.58v-31.57c0,.82-3.15,3.41-3.15,5.12v31.57c0-.82,3.15-3.41,3.15-5.12Z'/%3e%3cpath%20class='st0'%20d='M126,65.7v31.57c0-.82,3.15-3.41,3.15-5.12v-31.57c0,.82-3.15,3.41-3.15,5.12Z'/%3e%3cpath%20class='st0'%20d='M129.33,17.66h12.05c2.84,0,9.58-1.26,11.88,1s.99,9.65.99,12.57v7.68c0,1.02.42,3.18-.08,4.16l2.45-3.87c-2.65,2.65-9.57,1.3-12.94,1.3h-8.3c-1.39,0-3.16.25-4.43-.41-3.26-1.69-1.8-9.82-1.8-12.75v-8.1c0-1.02-.42-3.18.08-4.16l-2.45,3.87c.61-.83,1.46-1.26,2.55-1.3,1.58-.26,2.24-5.26,3.12-5.4-3.66.59-6.28,5.78-6.45,9.21-.22,4.32,0,8.71,0,13.04,0,2.56-1.14,8.91,1.38,10.74,2.38,1.74,8.02.64,10.7.64,4.09,0,8.55.52,12.6,0,3.59-.47,6.32-5.2,6.72-8.62.43-3.75,0-7.82,0-11.59,0-3.24.49-6.9-.02-10.11-.78-4.91-8.46-3.32-12.05-3.32h-12.87c-1.39,0-2.53,5.4-3.12,5.4v.02h-.01Z'/%3e%3cpath%20class='st0'%20d='M132.66,27.63h14.95c1.39,0,2.53-5.4,3.12-5.4h-14.95c-1.39,0-2.53,5.4-3.12,5.4Z'/%3e%3cpath%20class='st0'%20d='M132.66,35.94h9.97c.61,0,1.57-2.09,1.83-2.54.12-.22,1.35-2.86,1.29-2.86h-9.97c-.61,0-1.57,2.09-1.83,2.54-.12.22-1.35,2.86-1.29,2.86Z'/%3e%3cpath%20class='st0'%20d='M126.01,84.12h14.94c1.32,0,2.63-.23,3.7.37,2.18,1.2,4.29,4.29,6.03,6.03.96.96,3.14,2.58,3.55,3.7.61,1.66,0,4.74,0,6.47v14.86l3.13-5.26h-24.87c-.96,0-3.07.22-3.36-.21-.71-1.06,0-5.18,0-6.4v-24.82c0,.82-3.15,3.41-3.15,5.12v31.57l.02.14h28.24c.86,0,3.13-4.45,3.13-5.26v-15.24c0-1.7.55-4.54,0-6.19-.41-1.23-2.13-2.41-3.04-3.32-1.96-1.96-4-4.78-6.31-6.31-1.16-.76-1.77-.63-3.34-.63h-15.58c-1.39,0-2.53,5.4-3.12,5.4h.02v-.02Z'/%3e%3c/svg%3e)
Give agents boundaries they can follow.
ONE checks an agent's identity and purpose each time it connects, so a valid credential alone cannot grant access.
View Solutions%20--%3e%3cdefs%3e%3cstyle%3e%20.st0%20{%20fill:%20%23111;%20}%20.st1%20{%20fill:%20%23f0c53f;%20}%20.st2%20{%20fill:%20none;%20stroke:%20%23111;%20stroke-miterlimit:%208;%20stroke-width:%205px;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st0'%20d='M25.89,109.92v-62l-3.77,6.33c12.67,6.67,25.33,13.33,38,20,.55.29,3.77-5.58,3.77-6.33v-20l-3.77,6.33c6,3.33,12,6.67,18,10l12.7,7.05c1.09.6,4.85,2.06,5.28,2.81.74,1.29,0,5.23,0,6.72v35.25l3.77-6.33H25.88c-1.67,0-3.05,6.5-3.75,6.5h74c1.04,0,3.77-5.36,3.77-6.33v-42l-.02-.17c-12-6.67-24-13.33-36-20-.53-.29-3.77,5.58-3.77,6.33v20l3.77-6.33c-12.67-6.67-25.33-13.33-38-20-.55-.29-3.77,5.58-3.77,6.33v62c0-.99,3.79-4.1,3.79-6.16,0,0-.01,0,0,0Z'/%3e%3cpath%20class='st0'%20d='M36.12,90.25h12c.73,0,1.89-2.52,2.2-3.06.15-.26,1.62-3.44,1.55-3.44h-12c-.73,0-1.89,2.52-2.2,3.06-.15.26-1.62,3.44-1.55,3.44Z'/%3e%3cpath%20class='st0'%20d='M60.12,90.25h12c.73,0,1.89-2.52,2.2-3.06.15-.26,1.62-3.44,1.55-3.44h-12c-.73,0-1.89,2.52-2.2,3.06-.15.26-1.62,3.44-1.55,3.44Z'/%3e%3cpath%20class='st0'%20d='M36.12,104.25h12c.73,0,1.89-2.52,2.2-3.06.15-.26,1.62-3.44,1.55-3.44h-12c-.73,0-1.89,2.52-2.2,3.06-.15.26-1.62,3.44-1.55,3.44Z'/%3e%3cpath%20class='st0'%20d='M60.12,104.25h12c.73,0,1.89-2.52,2.2-3.06.15-.26,1.62-3.44,1.55-3.44h-12c-.73,0-1.89,2.52-2.2,3.06-.15.26-1.62,3.44-1.55,3.44Z'/%3e%3cpath%20class='st0'%20d='M41.89,47.92V11.92l-3.77,6.33h16.3c1.26,0,3.59-.46,4.81,0,.89.33.53-.28.87.2.3.42,0,2.23,0,2.73v52.9c0-.99,3.79-4.1,3.79-6.16V11.92l-.02-.17h-22c-1.04,0-3.77,5.36-3.77,6.33v36c0-.99,3.79-4.1,3.79-6.16Z'/%3e%3cpath%20class='st2'%20d='M98,83h38'/%3e%3cpath%20class='st1'%20d='M116,95c6.63,0,12-5.37,12-12s-5.37-12-12-12-12,5.37-12,12,5.37,12,12,12Z'/%3e%3cpath%20class='st0'%20d='M138.12,48.25h19.26c4.95,0,10.59-.99,10.72,5.51.3,14.68,0,29.4,0,44.08v10.34c0,1.16.47,3.55-.1,4.66l2.95-4.66c-2.14,2.14-5.33,1.57-8.11,1.57h-12.85c-4.89,0-11.88,1.48-12.09-5.17-.47-14.63,0-29.35,0-43.99v-10.5c0-1.2-.49-3.77.1-4.93l-2.95,4.66c.74-1,1.76-1.52,3.07-1.57,1.9-.31,2.7-6.33,3.75-6.5-5.98.96-7.77,8.82-7.77,13.98v50.42c0,4.88-.79,9.95,5.68,10.09,7.8.17,15.79.39,23.58,0,5.46-.28,8.46-7.3,8.53-12.2.26-16.49,0-33,0-49.49,0-5.14,1.65-12.63-5.43-12.81-8.18-.21-16.4,0-24.59,0-1.67,0-3.05,6.5-3.75,6.5h0Z'/%3e%3cpath%20class='st0'%20d='M144.12,64.25h14c.73,0,1.89-2.52,2.2-3.06.15-.26,1.62-3.44,1.55-3.44h-14c-.73,0-1.89,2.52-2.2,3.06-.15.26-1.62,3.44-1.55,3.44Z'/%3e%3cpath%20class='st0'%20d='M144.12,76.25h14c.73,0,1.89-2.52,2.2-3.06.15-.26,1.62-3.44,1.55-3.44h-14c-.73,0-1.89,2.52-2.2,3.06-.15.26-1.62,3.44-1.55,3.44Z'/%3e%3cpath%20class='st0'%20d='M144.12,100.25h14c.73,0,1.89-2.52,2.2-3.06.15-.26,1.62-3.44,1.55-3.44h-14c-.73,0-1.89,2.52-2.2,3.06-.15.26-1.62,3.44-1.55,3.44Z'/%3e%3c/svg%3e)
Protection fitted to the system it serves.
ONE configures and tests the rules for each environment, from a small device to a large compute system.
View Solutions%20--%3e%3cdefs%3e%3cstyle%3e%20.st0%20{%20fill:%20%23111;%20}%20.st1%20{%20fill:%20%23f0c53f;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st0'%20d='M31.63,22.83h62.5c5.63,0,12.66-.49,14.25,6.61.56,2.45.23,5.31.23,7.79v25.28c0,2.33.29,4.99-.25,7.29.28-1.21,1.5-1-.17-.48-.8.25-1.47.79-2.28,1.03-.98.29-1.94.35-2.95.4-.72.04-1.44,0-2.15,0h-34.96c-2.11,0-2.27,0-3.87,1.41l-10.32,9.18c-.99.89-2.5,2.87-3.75,3.34-.51.19-.3.44-.37.38-.21-.16,0-1.8,0-2.06v-12.09l-.02-.15c-4.98,0-12.34,1.34-16.93-.97-5.65-2.84-4.54-9.95-4.54-15.2v-21.09c0-2.22-.04-4.44,0-6.66,0-.62.13-1.32.06-1.92.38-1.51.23-1.52-.47-.03l.81-.63c1.96-.62,3.06-1.32,5.17-1.43,1.57-.08,2.62-5.77,3.36-5.82-15.58.81-12.33,23.68-12.33,33.87,0,5.49-.27,11.05,0,16.54.48,9.98,9.57,9.13,17,9.13.62,0,3.98-.47,4.45-.04.38.34.04,2.98.04,3.6v10.61c-.03.17.03.2.15.09,4.96-4.41,9.74-9.25,14.98-13.31,3.03-2.35,10.13-.95,14.09-.95h23.85c2.38,0,4.77.1,6.97-1.02,3.46-1.76,6.03-6.46,7.19-10.02,1.83-5.61.6-13.04.6-18.81,0-6.8.27-13.67,0-20.47-.3-7.44-5.72-9.22-12-9.22H35c-1.5,0-2.73,5.82-3.36,5.82h-.01Z'/%3e%3cpath%20class='st0'%20d='M51.33,42.53h37.6c1.5,0,2.73-5.82,3.36-5.82h-37.6c-1.5,0-2.73,5.82-3.36,5.82Z'/%3e%3cpath%20class='st0'%20d='M51.33,55.06h28.65c1.5,0,2.73-5.82,3.36-5.82h-28.65c-1.5,0-2.73,5.82-3.36,5.82Z'/%3e%3cpath%20class='st0'%20d='M88.93,92.67h34.52c1.33,0,3.5-.43,4.76,0s2.57,2.19,3.54,3.04c4.23,3.76,8.46,7.52,12.69,11.28.22.2,3.38-4.94,3.38-5.67v-14.33l-3.38,5.67c7.25,0,16.45,1.93,21.09-4.94,4.64-6.88,3.78-13.22,3.78-20.91v-14.28c0-2.55.31-5.47-.41-7.95-2.38-8.1-13.42-6.08-19.89-6.08h-24.48c-1.5,0-2.73,5.82-3.36,5.82,11.89,0,23.91-.52,35.79,0,9.8.43,8.96,9.51,8.96,16.7s.12,14.59,0,21.87v.66c0,.25-.07.98-.06,1.23-.35,1.31-.3,1.5.14.58.47-.65.45-.73-.08-.24-.54-.12-1.9,1.1-2.69,1.34-.95.29-1.89.35-2.87.4-.39.02-.8,0-1.19,0-3.78.04-7.57,0-11.34,0-.93,0-3.38,4.8-3.38,5.67v14.33l3.38-5.67-12.69-11.28c-.98-.87-2.3-2.63-3.54-3.04-1.24-.41-3.46,0-4.76,0h-34.52c-1.5,0-2.73,5.82-3.36,5.82l-.02-.03h-.01Z'/%3e%3cpath%20class='st1'%20d='M123.74,83.49c5.93,0,10.74-4.81,10.74-10.74s-4.81-10.74-10.74-10.74-10.74,4.81-10.74,10.74,4.81,10.74,10.74,10.74Z'/%3e%3c/svg%3e)
Share the message. Keep the terms.
Set who can use a message or file, for what purpose and for how long. Its terms travel with it.
View Solutions%20--%3e%3cdefs%3e%3cstyle%3e%20.st0%20{%20fill:%20%23111;%20}%20.st1%20{%20stroke-miterlimit:%208;%20}%20.st1,%20.st2%20{%20fill:%20none;%20stroke:%20%23111;%20stroke-linecap:%20round;%20stroke-width:%204px;%20}%20.st3%20{%20fill:%20%23f0c53f;%20}%20.st2%20{%20stroke-linejoin:%20round;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st2'%20d='M26,63h52M66,75l12-12-12-12'/%3e%3cpath%20class='st3'%20d='M102,83c11.05,0,20-8.95,20-20s-8.95-20-20-20-20,8.95-20,20,8.95,20,20,20Z'/%3e%3cpath%20class='st1'%20d='M94,55l16,16M110,55l-16,16'/%3e%3cpath%20class='st0'%20d='M128.11,20.08v92c0-.99,3.79-4.1,3.79-6.16V13.92c0,.99-3.79,4.1-3.79,6.16Z'/%3e%3cpath%20class='st0'%20d='M145.37,65.21h18.7c-.2,0-2.83-6.43-3.25-6.43h-18.7c.2,0,2.83,6.43,3.25,6.43Z'/%3e%3c/svg%3e)
Stopped before it acts
A connection that fails its conditions is refused before data moves.
%20--%3e%3cdefs%3e%3cstyle%3e%20.st0%20{%20fill:%20%23111;%20}%20.st1%20{%20fill:%20%23f0c53f;%20}%20.st2%20{%20fill:%20none;%20stroke:%20%23111;%20stroke-linecap:%20round;%20stroke-linejoin:%20round;%20stroke-width:%204px;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st0'%20d='M22.12,44.25h17.16c1.99,0,4.82-.47,6.65.49,2.43,1.28,2.17,3.71,2.17,6.01v29.46c0,1.14.46,3.53-.1,4.63l2.95-4.66c-2.13,2.13-5.15,1.57-7.91,1.57h-11.01c-1.96,0-4.21.31-6.16,0-3.55-.56-3.98-2.99-3.98-5.97v-29.99c0-1.12-.46-3.54.1-4.63l-2.95,4.66c.74-1,1.76-1.52,3.07-1.57,1.9-.31,2.7-6.33,3.75-6.5-4.54.73-7.59,7.16-7.77,11.38-.24,5.63,0,11.32,0,16.95s-.18,11.19,0,16.77c.16,5.22,3.73,5.4,8.04,5.4,5.74,0,11.76.54,17.47,0,4.57-.43,7.89-6.36,8.28-10.65.98-10.82,0-22.15,0-33.01,0-1.69.27-3.75-.79-5.19-1.61-2.19-4.88-1.64-7.24-1.64h-17.98c-1.67,0-3.05,6.5-3.75,6.5h0Z'/%3e%3cpath%20class='st0'%20d='M144.12,44.25h17.16c1.99,0,4.82-.47,6.65.49,2.43,1.28,2.17,3.71,2.17,6.01v29.46c0,1.14.46,3.53-.1,4.63l2.95-4.66c-2.13,2.13-5.15,1.57-7.91,1.57h-11.01c-1.96,0-4.21.31-6.16,0-3.55-.56-3.98-2.99-3.98-5.97v-29.99c0-1.12-.46-3.54.1-4.63l-2.95,4.66c.74-1,1.76-1.52,3.07-1.57,1.9-.31,2.7-6.33,3.75-6.5-4.54.73-7.59,7.16-7.77,11.38-.24,5.63,0,11.32,0,16.95s-.18,11.19,0,16.77c.16,5.22,3.73,5.4,8.04,5.4,5.74,0,11.76.54,17.47,0,4.57-.43,7.89-6.36,8.28-10.65.98-10.82,0-22.15,0-33.01,0-1.69.27-3.75-.79-5.19-1.61-2.19-4.88-1.64-7.24-1.64h-17.98c-1.67,0-3.05,6.5-3.75,6.5h0Z'/%3e%3cpath%20class='st2'%20d='M57.48,63h78.52M125.76,75l10.24-12-10.24-12'/%3e%3cpath%20class='st1'%20d='M92.4,75c7.89,0,14.29-6.4,14.29-14.29s-6.4-14.29-14.29-14.29-14.29,6.4-14.29,14.29,6.4,14.29,14.29,14.29Z'/%3e%3cpath%20class='st2'%20d='M85.25,60.71l5.56,5.56,9.52-11.11'/%3e%3c/svg%3e)
No extra inspection route
Enforcement is built into the handshake.
%20--%3e%3cdefs%3e%3cstyle%3e%20.st0%20{%20fill:%20%23111;%20}%20.st1%20{%20fill:%20%23f0c53f;%20}%20.st2%20{%20fill:%20none;%20stroke:%20%23111;%20stroke-linecap:%20round;%20stroke-linejoin:%20round;%20stroke-width:%204px;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st0'%20d='M64.9,21.51h36.51c1.04,0,2.85-.37,3.84,0,.87.32,1.8,1.67,2.45,2.33,2.15,2.15,4.3,4.3,6.44,6.44,1.67,1.67,3.67,3.28,5.14,5.14.53.67.35.07.43,1.17.25,3.4,0,6.92,0,10.33v52.49c0,2.13-.36,4.63,0,6.75,0,0-.06.9-.06.91l1.13-1.95c1.51-1.95,1.66-2.45.44-1.48-1.15.31-1.9.73-3.12.8-.24.01-.48,0-.71,0-1.55.03-3.1,0-4.65,0h-35.27c-2.94,0-6.53.54-9.43-.23-4.48-1.19-4.75-5.29-4.75-9.03v-12.35c0-20.81-.4-41.66,0-62.47,0-.17.03-.38,0-.55-.61-3.64-1.32,4-2.21,2.98-.27-.31,3.27-1.22,3.81-1.26,1.01-.07,2.43-3.23,2.87-4,.21-.36,2.04-4.48,2.02-4.48-5.11.33-7.61,5.28-9.7,9.38-.99,1.94-1.71,3.8-1.75,5.98-.07,3.26,0,6.52,0,9.77v38.21c0,9.6-.1,19.19,0,28.79.05,4.42,2.4,7.65,7.1,7.74,4.38.08,8.77,0,13.15,0,11.26,0,22.54.18,33.8,0,2.23-.04,4.17-.53,5.82-2.16,2.98-2.97,6.2-8.34,6.44-12.63.14-2.44,0-4.93,0-7.37V30.05c0-.65.22-1.76,0-2.38-.37-1.08-1.91-2.13-2.72-2.94l-6.75-6.75c-1.3-1.3-3.11-4.01-4.8-4.8-.65-.31-1.7-.12-2.43-.12h-38.16c-.95,0-2.47,3.29-2.87,4-.2.34-2.12,4.48-2.02,4.48h.01v-.02h0Z'/%3e%3cpath%20class='st0'%20d='M106.59,19.28v14.47h14.37c1.09,0,1.99-4.24,2.45-4.24h-11.9c-.29,0-2.25.21-2.44.04-.18-.16,0-1.84,0-2.18v-12.12c0-.32-1.04,1.21-1.12,1.33-.41.66-1.36,1.86-1.36,2.7Z'/%3e%3cpath%20class='st0'%20d='M71.55,52.03h20.89c1.09,0,1.99-4.24,2.45-4.24h-20.89c-1.09,0-1.99,4.24-2.45,4.24Z'/%3e%3cpath%20class='st0'%20d='M71.55,69.01h20.89c1.09,0,1.99-4.24,2.45-4.24h-20.89c-1.09,0-1.99,4.24-2.45,4.24Z'/%3e%3cpath%20class='st1'%20d='M104.22,92.72c5.15,0,9.33-4.18,9.33-9.33s-4.18-9.33-9.33-9.33-9.33,4.18-9.33,9.33,4.18,9.33,9.33,9.33Z'/%3e%3cpath%20class='st2'%20d='M123.52,68.22h18.28M133.96,76.06l7.83-7.83-7.83-7.83'/%3e%3c/svg%3e)
Protection travels
An encrypted object carries the owner's terms.
%20--%3e%3cdefs%3e%3cstyle%3e%20.st0%20{%20fill:%20%23111;%20}%20.st1%20{%20fill:%20%23f0c53f;%20}%20.st2%20{%20fill:%20none;%20stroke:%20%23111;%20stroke-linecap:%20round;%20stroke-linejoin:%20round;%20stroke-width:%204px;%20}%20%3c/style%3e%3c/defs%3e%3cpath%20class='st0'%20d='M66.39,22.14h34.91c.99,0,2.72-.35,3.67,0,.84.31,1.72,1.6,2.35,2.23,2.05,2.05,4.11,4.11,6.16,6.16,1.6,1.6,3.51,3.13,4.91,4.91.51.64.33.07.41,1.12.24,3.25,0,6.62,0,9.88v50.19c0,2.04-.34,4.43,0,6.45,0,0-.06.86-.06.87l1.08-1.86c1.45-1.87,1.59-2.34.42-1.42-1.1.3-1.82.7-2.98.76-.22.01-.46,0-.68,0-1.48.02-2.97,0-4.44,0h-33.73c-2.82,0-6.24.51-9.01-.22-4.28-1.14-4.54-5.06-4.54-8.64v-11.81c0-19.9-.39-39.84,0-59.73,0-.16.02-.36,0-.52-.58-3.48-1.26,3.82-2.11,2.85-.26-.29,3.13-1.17,3.65-1.2.97-.06,2.32-3.09,2.75-3.82.2-.34,1.95-4.29,1.94-4.29-4.89.32-7.28,5.05-9.28,8.97-.94,1.85-1.64,3.63-1.67,5.72-.06,3.11,0,6.23,0,9.34v36.54c0,9.18-.09,18.35,0,27.53.04,4.23,2.29,7.32,6.79,7.4,4.19.08,8.38,0,12.57,0,10.77,0,21.55.17,32.32,0,2.13-.04,3.99-.51,5.56-2.07,2.85-2.84,5.93-7.98,6.16-12.08.13-2.33,0-4.71,0-7.05V30.31c0-.62.21-1.68,0-2.28-.35-1.04-1.82-2.03-2.6-2.81l-6.45-6.45c-1.24-1.24-2.98-3.83-4.59-4.59-.62-.29-1.62-.12-2.33-.12h-36.49c-.91,0-2.36,3.15-2.75,3.82-.19.32-2.02,4.29-1.94,4.29h.01v-.02h-.01Z'/%3e%3cpath%20class='st0'%20d='M73.25,51.32h31.35c1.64,0,2.99-4.06,3.68-4.06h-31.35c-1.64,0-2.99,4.06-3.68,4.06Z'/%3e%3cpath%20class='st0'%20d='M73.25,83.78h21.55c1.64,0,2.99-4.06,3.68-4.06h-21.55c-1.64,0-2.99,4.06-3.68,4.06Z'/%3e%3cpath%20class='st0'%20d='M73.25,67.55h31.35c1.64,0,2.99-4.06,3.68-4.06h-31.35c-1.64,0-2.99,4.06-3.68,4.06Z'/%3e%3cpath%20class='st1'%20d='M123,90.23c4.93,0,8.92-3.99,8.92-8.92s-3.99-8.92-8.92-8.92-8.92,3.99-8.92,8.92,3.99,8.92,8.92,8.92Z'/%3e%3cpath%20class='st2'%20d='M122.64,76.94v4.57l3.65,2.74'/%3e%3c/svg%3e)
Evidence as it happens
Openings, refusals and expires can be witnessed as they occur.